CRISC Certification 2026: Cost, Requirements & Who It’s For
• Nathaniel Miller
The CRISC certification exam costs $575 for ISACA members and $760 for non-members, plus a $50 application fee once you pass. Certification requires three years of IT risk experience across at least two of the four CRISC domains. The exam is 150 questions in four hours, scored 200 to 800, and you need 450 to pass.
CRISC (Certified in Risk and Information Systems Control) is ISACA’s IT risk management credential. It sits alongside CISM, which is for security managers, and CISA, which is for auditors. Below: the full cost, the requirements, what’s on the exam, and whether it’s the right ISACA certification for you.
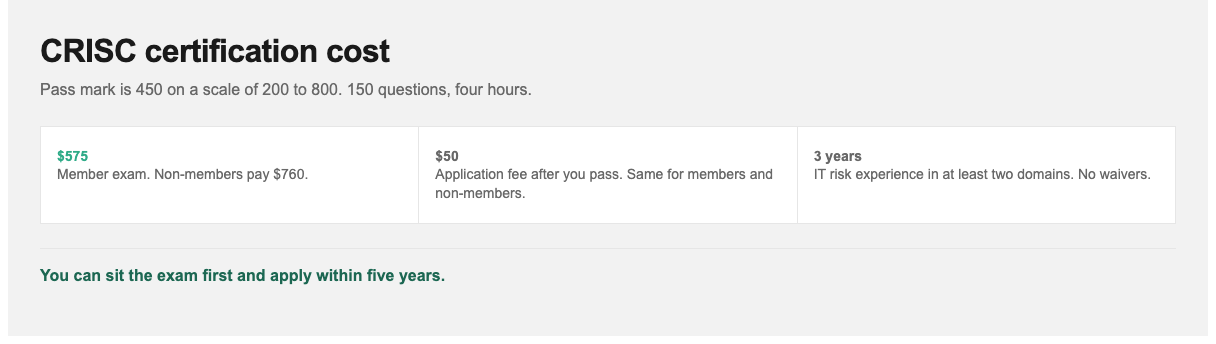
Membership discount on the exam is $185. Professional membership is about $145 to join.
CRISC Cost: Every Fee
| Fee | ISACA member | Non-member |
|---|---|---|
| Exam registration | $575 | $760 |
| Certification application (after passing) | $50 | $50 |
| Annual maintenance fee | $45 | $85 |
| Minimum to certify | $670 | $895 |
Does ISACA membership pay for itself? Professional membership costs about $145 to join and $135 a year after that, plus local chapter dues. The member exam discount is $185, so membership roughly breaks even on the exam alone. It comes out clearly ahead once you add the lower maintenance fee and member pricing on the official review manual and practice question database.
Budget separately for preparation. The official review manual costs about $120 to $150, the practice question database about $300, and instructor-led training more.
CRISC Requirements
- Three years of relevant work experience in IT risk management and IS control.
- Experience must cover at least two of the four CRISC domains.
- Experience must fall within the 10 years before you apply.
- No waivers or substitutions, unlike CISM and CISA, which accept some education-based waivers.
- You can take the exam first and gain the experience afterwards. You then have five years from passing to apply.
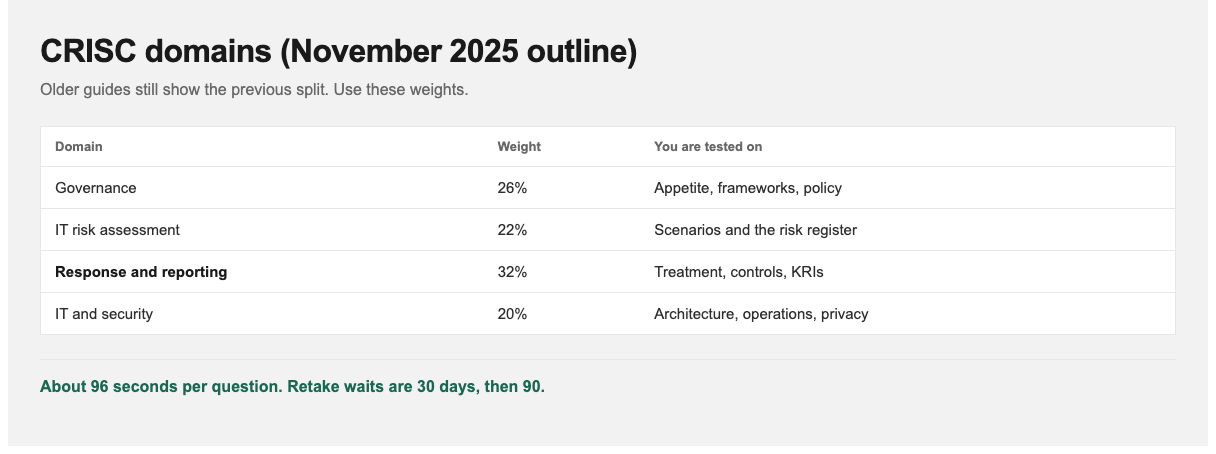
Domain 3 is the largest, and it is where the risk-practitioner judgment shows up.
What’s on the CRISC Exam
| Domain | Weight | Covers |
|---|---|---|
| 1. Governance | 26% | Organizational governance, risk appetite and tolerance, risk management frameworks, policies |
| 2. IT Risk Assessment | 22% | Risk identification, threat and vulnerability analysis, risk scenarios, risk registers |
| 3. Risk Response and Reporting | 32% | Risk treatment options, control design and ownership, KRIs and KPIs, reporting to leadership |
| 4. Information Technology and Security | 20% | Enterprise architecture, IT operations, project and change management, security principles, data privacy |
These weights follow the exam content outline that took effect in November 2025. Many older guides still show the previous split. Domain 3 is the biggest, and it is where the exam’s “best answer from a risk practitioner’s view” style is most noticeable.
- Format: 150 multiple-choice questions, 4 hours, about 96 seconds per question.
- Delivery: PSI test center or remote proctored. Registration is open continuously, and you have a six-month window to sit the exam.
- Retakes: wait 30 days after a first failure, then 90 days. Maximum four attempts in 12 months.
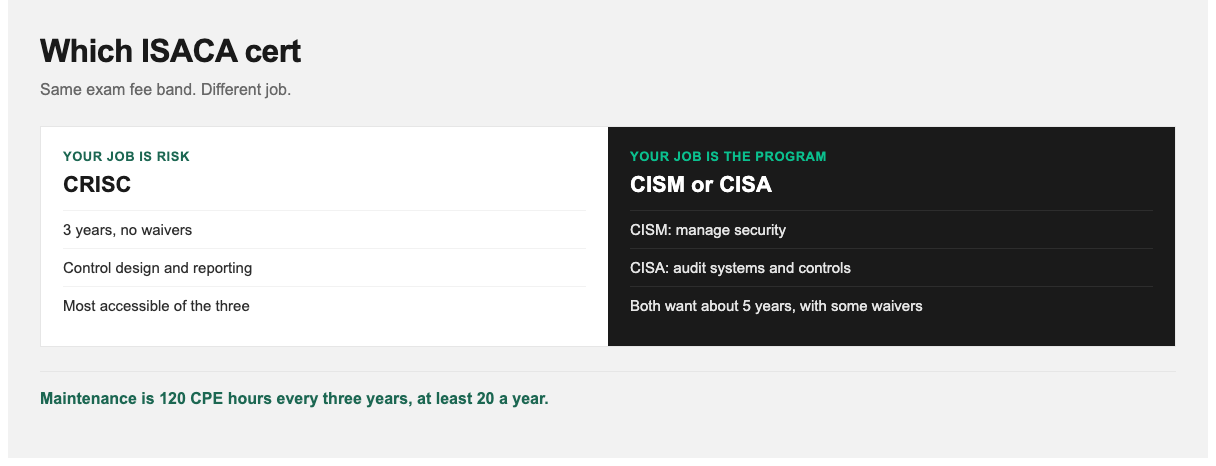
CRISC if you own the risk register. CISM if you run the security function. CISA if you audit it.
CRISC vs CISM vs CISA
| CRISC | CISM | CISA | |
|---|---|---|---|
| Focus | Identifying and treating IT risk | Managing an information security program | Auditing IT systems and controls |
| Typical roles | IT risk manager, GRC analyst, control owner | Security manager, aspiring CISO | IT auditor, assurance |
| Experience | 3 years, no waivers | 5 years (3 in security management), some waivers | 5 years, some waivers |
| Exam fee | $575 / $760 | $575 / $760 | $575 / $760 |
Choose CRISC if risk is your job rather than one task within it, for example if you own the risk register, report to a risk committee or design controls. Choose CISM if you run or want to run a security function. See our CISM guide. Many GRC professionals eventually hold two of the three.
Is CRISC Worth It?
For people in IT risk and governance roles, yes. ISACA has reported average salaries for CRISC holders above $150,000. It is also one of the few credentials aimed squarely at the risk function rather than security operations or audit. Its shorter experience requirement (three years against five for CISM and CISA) also makes it the most accessible ISACA management-level credential.
It’s less useful for hands-on technical roles. If you configure firewalls or respond to incidents, a technical certification will do more for you. Our guide to the best cybersecurity certifications in 2026 maps the alternatives by career stage.
Maintaining CRISC
Earn 120 CPE hours every three years, with at least 20 each year, and pay the annual maintenance fee ($45 member, $85 non-member). Most risk professionals earn CPE through work-related training, webinars and ISACA chapter events.
How StormWind Studios Approaches CRISC
The CRISC exam tests judgment, meaning which response a risk practitioner would choose, more than memorized facts. StormWind’s live CRISC course works through scenario questions in each domain with instructors who have run real risk programs. Teams building wider governance capability can pair it with NIST CSF 2.0: Frameworks, Governance and Continuous Improvement, or with CISM for the security management side.
Frequently Asked Questions
How much does the CRISC exam cost?
$575 for ISACA members and $760 for non-members, plus a $50 application fee after you pass.
What are the CRISC requirements?
Three years of IT risk and control experience covering at least two of the four domains, earned within the last 10 years. No waivers are available.
Can I take CRISC without experience?
Yes. You can pass the exam first and then have up to five years to gain the experience and apply.
What is the CRISC passing score?
450 on a scaled score of 200 to 800.
Is CRISC harder than CISM?
They have the same format and similar difficulty. Which one feels harder depends on your background: risk practitioners tend to find CRISC more intuitive, and security managers tend to find CISM easier.
How long is CRISC valid?
CRISC stays active as long as you earn 120 CPE hours per three-year cycle (minimum 20 a year) and pay the annual maintenance fee.